
Cyberattack by the UAC-0010 (Armageddon) Group on Ukrainian State Organizations (CERT-UA#4378)
General information
The Government Computer Emergency Response Team of Ukraine, CERT-UA, has detected the distribution of emails with the subject "Information about Russian war criminals" among Ukrainian state bodies. The email contains an HTML file "Військові злочинці РФ.htm", opening which will create a RAR archive "Viyskovi_zlochinci_RU.rar" on the computer. The archive contains a shortcut file "Військові-злочинці що знищують Україну (домашні адреси, фото, номера телефонів, сторінки у соціальних сетях).lnk", opening which will download an HTA file containing VBScript code, which in turn will download and run the PowerShell script "get.php" (GammaLoad.PS1). The latter's task is to determine the computer's unique identifier (based on the computer name and the serial number of the system drive), send this information to the command-and-control server via an HTTP POST request for use as an XOR key, and then download, XOR-decode and run the payload.
The activity is associated with the UAC-0010 (Armageddon) group.
We draw attention to the need for additional checking of emails with attachments in the form of HTM files, since their detection rate is currently low.
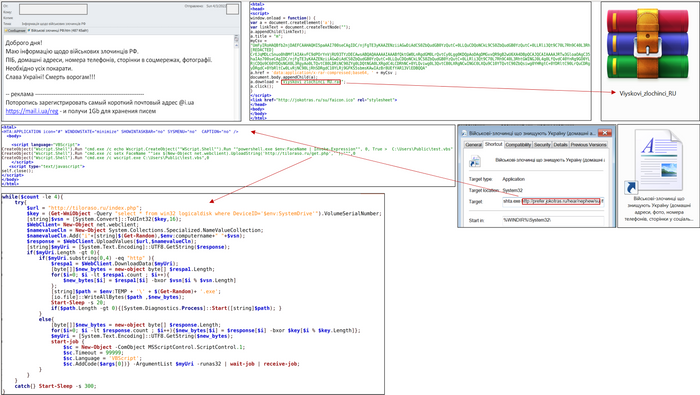
Photo: cert.gov.ua


