
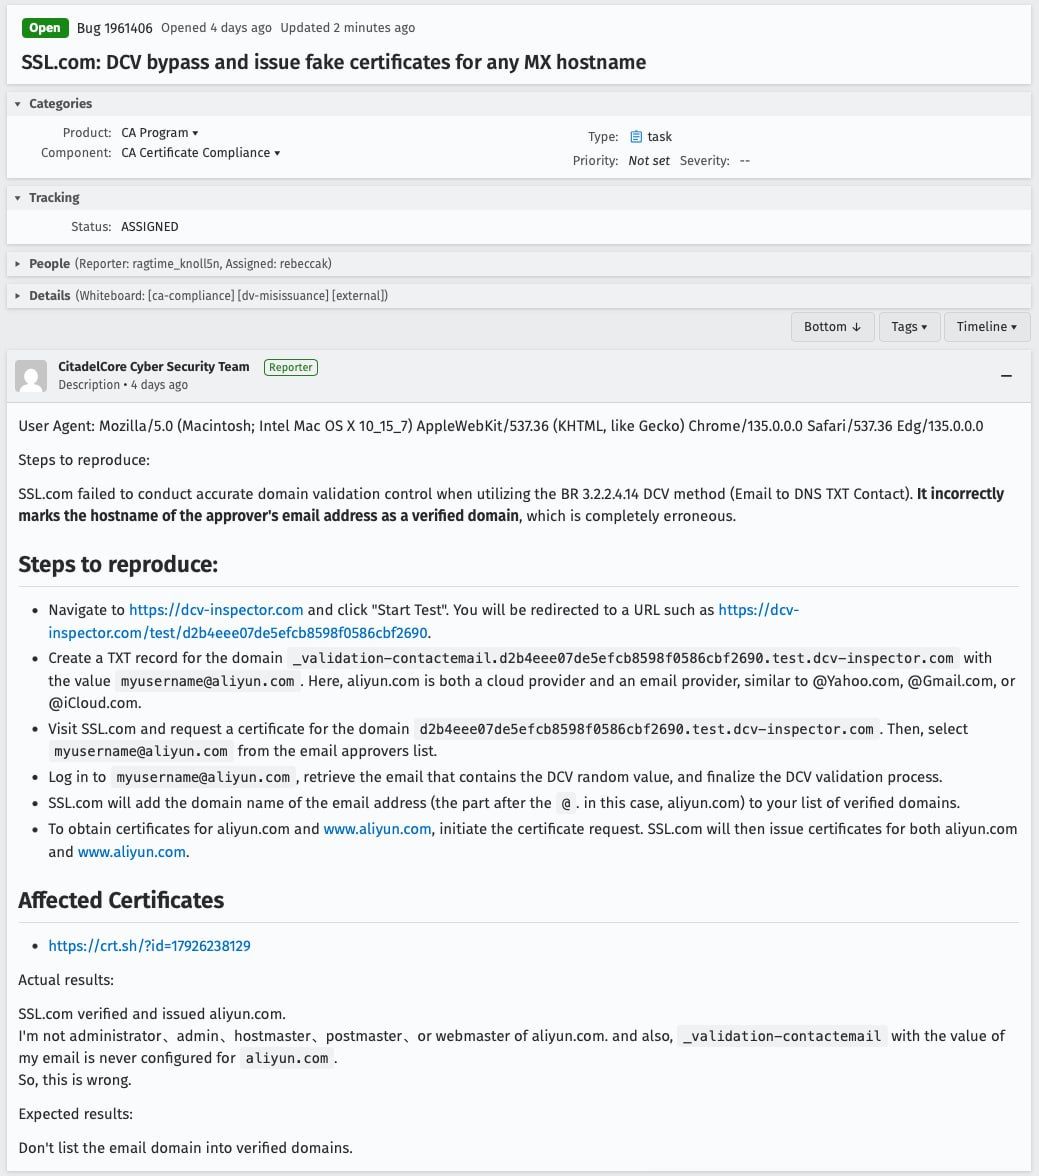
SSL.com: DCV Bypass and Issuance of Forged Certificates for Any MX Host
Today SSL.com found itself in the spotlight because of a vulnerability discovered by a researcher (link) that makes it possible to issue a forged TLS certificate for any domain.
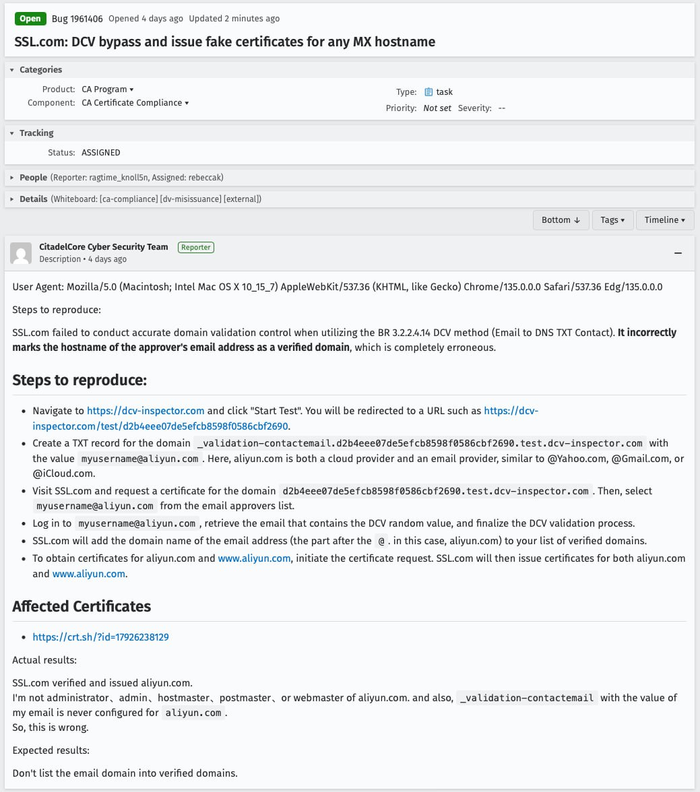
• The vulnerability was caused by a bug in the implementation of domain control validation via email confirmation. For email validation, a DNS TXT record _validation-contactemail must be added to the DNS zone of the domain for which the certificate is requested. For example, _validation-contactemail.test.com DNS TXT name@example.com. After the domain validation is initiated, a confirmation code is sent to the email name@example.com; entering it confirms control of the domain "test.com" and allows obtaining a TLS certificate for "test.com".
• The essence of the vulnerability was that, besides the domain "test.com" for which the certificate was requested, the ownership validation was also considered valid for the domain "example.com" used in the email address. The researcher who found the problem demonstrated obtaining a valid TLS certificate for the domain aliyun.com, which is used in the mail service of the Chinese company Alibaba. During the test attack, the researcher registered the validation domain d2b4eee07de5efcb8598f0586cbf2690.test.dcv-inspector.com in the dcv-inspector.com service and requested a TLS certificate for it, adding the DNS record:
_validation-contactemail.d2b4eee07de5efcb8598f0586cbf2690.test.dcv-inspector.com DNS TXT myusername@aliyun.com
• After that, on the SSL.com website he requested a TLS certificate for d2b4eee07de5efcb8598f0586cbf2690.test.dcv-inspector.com and chose email validation. A confirmation code was then sent to myusername@aliyun.com, and after entering it, not only d2b4eee07de5efcb8598f0586cbf2690.test.dcv-inspector.com but also aliyun.com ended up in the list of verified domains. As a result, the researcher successfully obtained a TLS certificate for the domain "aliyun.com", ownership of which was thus "confirmed".
• SSL.com has already acknowledged the bug and started working on a fix. A detailed report is promised by 2 May. It promises to be interesting =)
#News


